How to Increase Scanner Timeout
A red Timeout on the Scans page means the scan ran longer than the time allowed for it. Scans of the default branch are limited by the Main Timeout and pull request scans by the PR Timeout, both set account-wide in the Global Scanner Configuration.
A scan that timed out can still complete: when its results arrive, the scan is updated.
Raise the Timeout in the Global Scanner Configuration
-
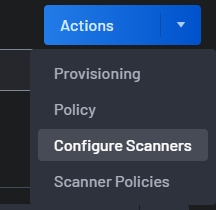
On the Scanner Coverage page, open the Actions menu at the top right and select Configure Scanners to open the Global Scanner Configuration.
-
Raise the Main Timeout if scans of the default branch time out, or the PR Timeout if pull request scans time out.
- Save the configuration.
For scanners provisioned with Zero Touch Provisioning (ZTP), raise these settings instead of editing the pipeline in the Boost scanner project: edits to that pipeline are overwritten when its template is updated.
Manually Provisioned Pipelines
The Main Timeout and PR Timeout don't apply to a scanner you provisioned manually in your own pipeline. Its scans run with the timeouts of the Boost Security CLI, in seconds:
| Scan | Default | Allowed values |
|---|---|---|
| Default branch | 7200 (2 hours) | 30 to 7200 |
| Pull request (diff scan) | 120 (2 minutes) | 30 to 1800 |
A default-branch scan can't run longer than 2 hours: its default is already the maximum.
To change a timeout, set the parameter of your CI/CD integration:
| Integration | Default branch | Pull request |
|---|---|---|
| GitHub Actions | scan_main_timeout |
scan_diff_timeout |
| Azure DevOps | scanMainTimeout |
scanDiffTimeout |
| GitLab | BOOST_MAIN_SCAN_TIMEOUT |
BOOST_DIFF_SCAN_TIMEOUT |
| Bitbucket | BOOST_MAIN_SCAN_TIMEOUT |
BOOST_DIFF_SCAN_TIMEOUT |
For example, with GitHub Actions, add the parameter under the with: section of the scanner step. This example lets pull request scans run for up to 20 minutes:
      - name: Run Boost Security Semgrep
        uses: boostsecurityio/boostsec-scanner-github@v4
        with:
          api_token: ${{ secrets.BOOST_API_TOKEN }}
          registry_module: boostsecurityio/semgrep
          scan_diff_timeout: 1200
See the full list of parameters for GitHub Actions, Azure DevOps and GitLab.
When the CI Job Itself Stops
A Boost Security timeout is different from a CI job stopped by your CI/CD system:
- The CI job hit its own time limit. Your CI/CD system cancels the job, and the scan often leaves no entry in the scan history. Raise the job time limit in your CI/CD system.
- Every scanner times out at once, the CI jobs are short, and they show no scanner output. This usually means the pipeline template was modified so that the job ends before the Boost Security CLI runs. Restore the unmodified template.